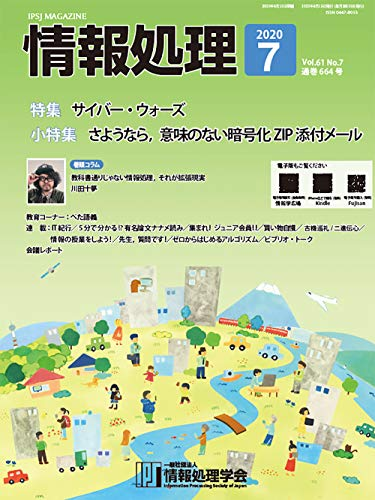
The special feature “Goodbye to Pointless Encrypted ZIP Email Attachments,” which we had been preparing since the end of last year for the Information Processing Society of Japan’s magazine Information Processing, has now been published.
Pointless encrypted ZIP email attachments refer to the distinctively Japanese custom commonly called PPAP. It is now used by government agencies and many companies.
After consulting Koichiro Eto of AIST, we arranged the feature as follows.
- 0. Editorial Introduction — Ritual Security PPAP: Toward a Japanese Security Renaissance
- 1. What Is PPAP? — Its Dark History of Development
- 2. The Security Significance of PPAP
- 3. Why Did We Come to Use PPAP?
- 4. Roundtable: “How Can We Eliminate PPAP from Society?”
- Nat Sakimura, Akira Otaishi, Masanori Kusunoki, and Tetsutaro Uehara
We had hoped to obtain a contribution from a cultural-anthropological perspective as Chapter 2, but unfortunately were unable to do so this time. Any cultural anthropologist who feels up to the task is invited to contact me.
Chapter 4 is the much-discussed roundtable “How Can We Eliminate PPAP from Society?” It contains many substantive, not merely crowd-pleasing, observations: why paper seals are meaningless today; why neither ISMS nor the PrivacyMark caused PPAP; and how we thought companies selling PPAP solutions might kill us, but nothing of the sort happened. Please read it.
It also includes a commemorative photo unique to a Zoom discussion. The highlight is reportedly that approximately one participant appears as a virtual-girl avatar.
If you are troubled by PPAP, I hope you will cite this feature and use it to break through the problem.
Related posts
Japan’s Financial Services Agency Calls on Financial Institutions to Review the Practice of Emailing Password-Protected ZIP Files (So-Called PPAP)
According to a May 22 report by The Nikkin, Japan's Financial Services Agency appears to have called on financial institutions to review the practice of emailing…
I Will Appear on the Okinawa Open Days Panel “Current and Future OSS Initiatives in Economic Security”
It is already the day of the event—in fact, I am writing this now (12/4 9:45) at my desk while preparing for the panel—but I will…
The “DS-511 Guidelines for Handling Digital Identity in Identity Verification for Administrative Procedures, etc.” Have Been Published
After 3 years of development, the Digital Identity Guidelines, to which I had the privilege of contributing as an expert (Expert Meeting on the Revision of…