I saw that Gina Trapani had written a blog post about Chris Messina’s “This Week in Google.” It explains how to use your own domain as an OpenID.
http://smarterware.org/6286/how-to-set-up-openid-on-your-own-domain/
In the comments, many people are delighted to discover, “OpenID can do that!” It is very good that people have been reminded how useful OpenID “delegation” is.
In the post, he writes:
I still haven’t figured out how to designate Idproxy as my “fallback” provider. If you know how, please tell me in the comments.
John Bradley posted a reply, but WordPress ate the tags in the comment and rendered it incomprehensible, so I will post my version here.
(1) Create an XRDS file like the following. Modify the contents as appropriate for your own situation.
<?xml version="1.0" encoding="UTF-8"?>
<xrds:XRDS xmlns:xrds="xri://$xrds" xmlns="xri://$xrd*($v*2.0)">
  <XRD>
    <CanonicalID>http://xri.net/=!E18C.3B56.889D.850B</CanonicalID>
    <Service priority="10">
      <Type>http://specs.openid.net/auth/2.0/signon</Type>
      <URI>https://authn.fullxri.com/authentication/</URI>
      <LocalID>http://xri.net/=!E18C.3B56.889D.850B</LocalID>
    </Service>
    <Service priority="20">
      <Type>http://specs.openid.net/auth/2.0/signon</Type>
      <URI>https://www.google.com/accounts/o8/ud?source=profiles</URI>
      <LocalID>http://www.google.com/profiles/sakimura</LocalID>
    </Service>
  </XRD>
</xrds:XRDS>
In this file, each <Service> represents an Authentication Service.
In the example above, Google (priority="20") is specified as the failover server for fullxri (priority="10").
(2) Specify the location of this file on the domain’s home page as shown below. (In this example, it is a file named yadis.xml placed at the top level of www.sakimura.org.)
<meta http-equiv="X-XRDS-Location" content="http://www.sakimura.org/yadis.xml"></meta>
That’s all!
Unfortunately, not every RP library supports this kind of failover. As far as I know, the DotNetOpenAuth and JanRain libraries appear to support it.
Related posts

W3C Standardizes Decentralized Identifiers: Looking Back at the History That Led There
I wrote the article named in the title for Nikkei XTECH about DID (Decentralized Identifier), for which W3C issued a Recommendation last week . It covers…
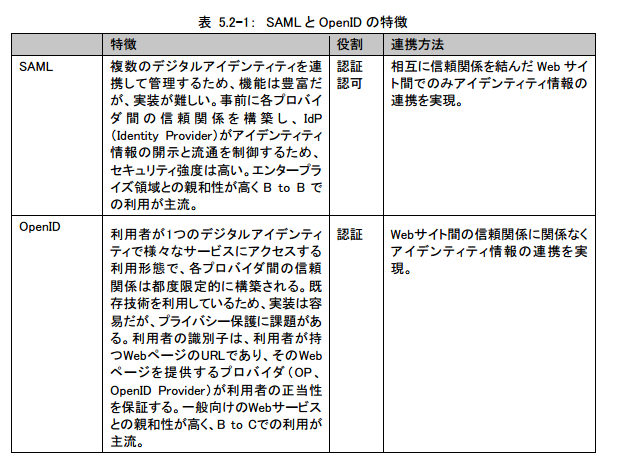
On the SAML/OpenID Comparison Table in IPA’s “Identity Management Technology Guide”
On August 9, the Information-technology Promotion Agency, Japan (IPA) released a draft of a textbook titled “Identity Management Technology Guide” [1]. The 8 edition is still…

DID and OpenID as Seen from the XRI Worldline—YouTube Stream
On February 8, 2024 from 11 p.m., I will be doing a YouTube stream titled “DID and OpenID as Seen from the XRI Worldline.” There was…